A smart contract is a program executed by a blockchain. A token is a record managed by a contract under a standard. Before interacting, verify the contract address, network, called functions, approvals, administrator powers and external dependencies.
The exact contract matters more than its name.
Code, interface and external data can diverge.
A standard or audit does not mean bug-free.
From code to execution
The contract receives a signed call, checks its conditions and changes its state. The website prepares the call but is not the final rule: a compromised domain can request a different function or contract.
Understand token standards
Standards describe common functions used to transfer, approve or query an asset. They improve interoperability but do not certify the issuer, value, legal rights or code quality.
- Check network and contract
- Identify sensitive functions
- Review events and metadata
Approvals, proxies and administrators
An approval may let a contract spend tokens up to a limit. A proxy may make logic upgradeable. Document administrator keys, delays, multisignatures and pause mechanisms.
Oracles and dependencies
A protocol may depend on a price feed, bridge, interface, sequencer or another contract. Map these dependencies and their failure scenarios before treating the service as autonomous.
- Data source
- Update frequency and delay
- Anomaly procedure
Read a contract’s powers
Public code is insufficient if an administrator can change the implementation or pause use. Check the contract address actually used and its upgrade permissions.
- Identify who may change parameters and after what delay.
- An audit covers a scope and version, not permanent safety.
Practical case: decision and limits
An app claims an audit, but its contract address differs from the report. Compare network, address, code version, date and audit scope. For an upgradeable proxy, identify the implementation and upgrade authority too. Explorer code verification concerns correspondence with deployed code; it does not establish safety or suitability.
A concrete verification
For a proxy, check current implementation and administrator, not only proxy-address code.
Decimals: separate quantity from presentation
An ERC-20 contract uses integers for balanceOf, transfer and allowance. The decimals metadata is for display; it creates neither returns nor value. Hypothetical example: 2500000 units with 6 decimals give 2.5 tokens; with 18, the same integer gives 0.0000000000025 tokens. ERC-20 allows decimals to be absent, so an interface must not invent a precision.
- Identify the contract and network before reading metadata.
- Preserve integer amounts as exact digits, without scientific notation or implicit rounding.
A stable address can conceal different code
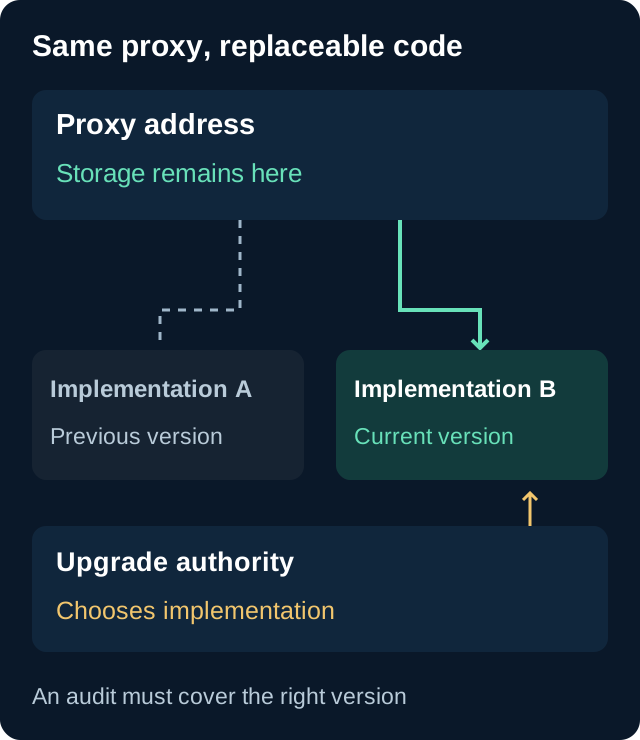
A proxy keeps its address and may delegate execution to a replaceable implementation. With delegatecall, implementation code operates in the proxy’s storage context. Storage compatibility and control over upgrades therefore matter.
- Identify who can change the implementation and through which procedure.
- An execution delay allows time to react; it does not guarantee a safe change.
Worked example: an audit of version A
A report covering version A does not automatically cover version B later installed behind the same proxy. The address shown in a wallet may nevertheless stay unchanged.
- Compare the current implementation, audited version and report scope.
- Review the upgrade history and remaining administrative powers.
Identify the implementation behind a proxy
For an ERC-1967-compatible proxy, an explorer can obtain the implementation from proxy storage or its beacon contract. Record the proxy address, the implementation address and the network. Identify who can change the implementation and whether a delay or quorum applies. The code can change while the proxy address stays the same. Recheck which implementation is active before a significant operation.
What to verify
| Element | Question | Risk |
|---|---|---|
| Address | Is this the official contract on the right network? | Imitation or wrong asset |
| Approval | Which operator and amount? | Unwanted future spending |
| Administration | Who can upgrade or pause? | Concentrated control |
| Oracle | Which external data is used? | False or stale price |
Convert token units without rounding
An ERC-20 balance is an integer. The decimals field tells you how to display it in tokens. Compare both representations before interpreting an amount or an allowance.
Without JavaScript, use the formulas and example below to move the decimal point manually.
Displayed amount = integer ÷ 10^d; integer = displayed amount × 10^d, where d is the number of decimals. Every digit is preserved. Results are normalized without thousands separators or unnecessary fractional zeroes.
Read decimals from the contract on the intended network: this metadata is optional in ERC-20. A symbol alone does not identify an asset. This tool verifies neither contract, balance, price nor net amount received. Calculation needs no wallet connection or network request.
Frequently asked questions
Is a contract immutable?
Not always. A proxy or administrative parameters can change its behavior.
Does disconnecting a wallet cancel approvals?
No. An on-chain approval usually remains active until revoked or expired under its own rules.
Is an audit enough?
No. It covers a scope, version and period, not every dependency or future change.
Verifiable sources
 Ethereum.org: Smart contracts
- Ethereum.org: Contract upgrades
- Ethereum.org: Token standards
- Ethereum.org: Security and scam prevention
- ERC-20: Token amounts, decimals and allowances
- OpenZeppelin: Proxy upgrade pattern
- ERC-1967: Proxy storage and implementation
Independent educational content reviewed against primary documentation. No personalized recommendation or promise of returns. Updated November 15, 2026
Prepare and continue reading
Useful background
- Understand blockchain simply
A blockchain is a shared ledger whose history is stored and checked by multiple computers. Transactions are signed, broadcast, verified and grouped into blocks under common rules. It does not make every user anonymous or every application safe.
- Message signatures: login, permits and permissions
No immediate paid transaction does not mean no risk. Inspect request type, domain, network, contract, spender, value and expiry. Reject requests whose scope your wallet cannot explain.
Continue to the next step
- Token approvals: review and revoke spending permissions
On each network, inspect approved spenders, token and limit. Revoke permissions you no longer need with a trusted tool, then verify the confirmed transaction. If a recovery phrase is exposed, revocation alone is insufficient.
- Smart accounts: recovery, fees and new risks
Check who can sign, recover, change rules and pay fees. A simpler interface does not remove contract or provider risk.