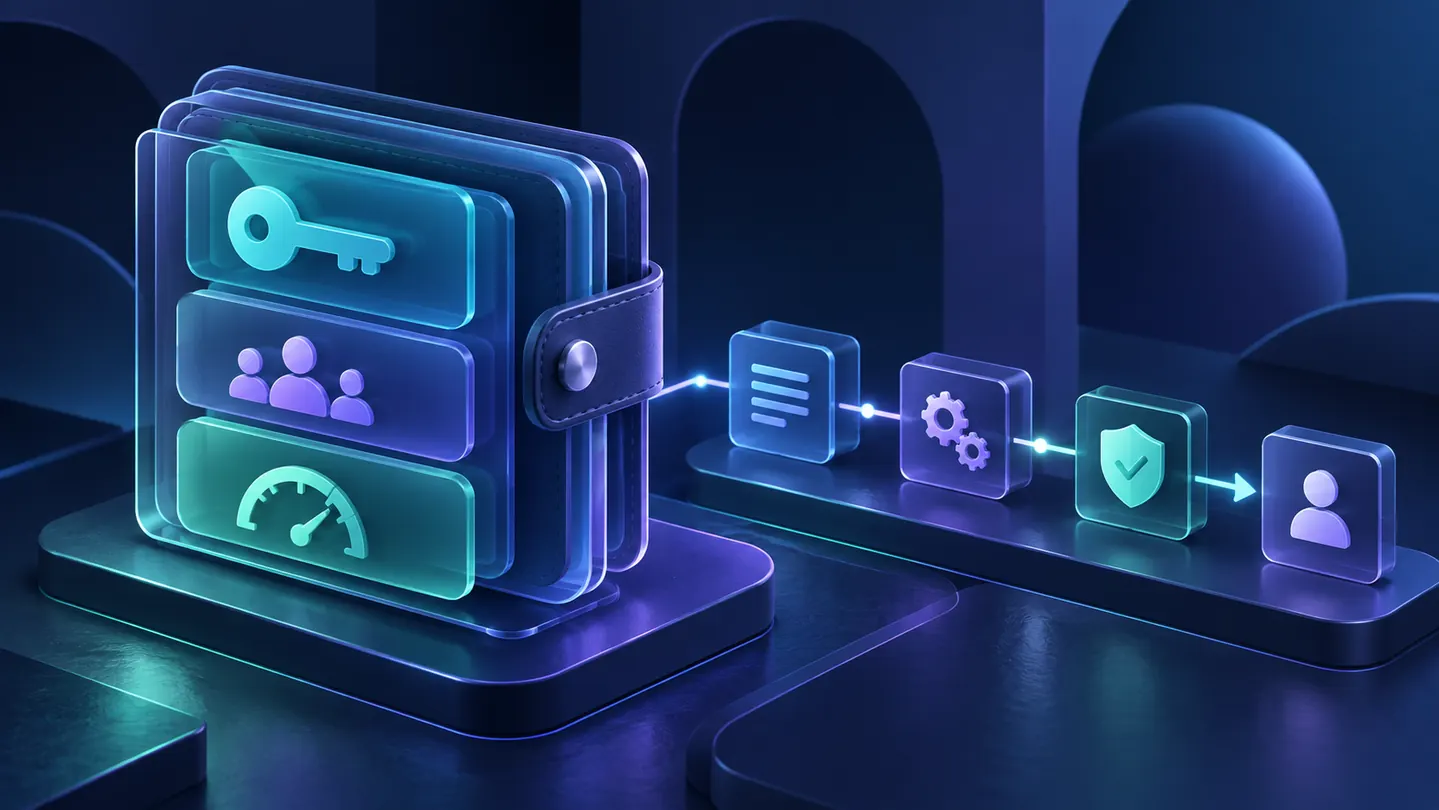
Check who can sign, recover, change rules and pay fees. A simpler interface does not remove contract or provider risk.
Identify signers
Test the process
Map dependencies
Signing rules
A smart account may require multiple approvals, spending limits or session keys. Read deployed rules rather than inferring safety from the interface.
Recovery
Identify guardians, delays, emergency powers and the procedure after losing a phone. Poor recovery design can lock funds or enable takeover.
Fees and relays
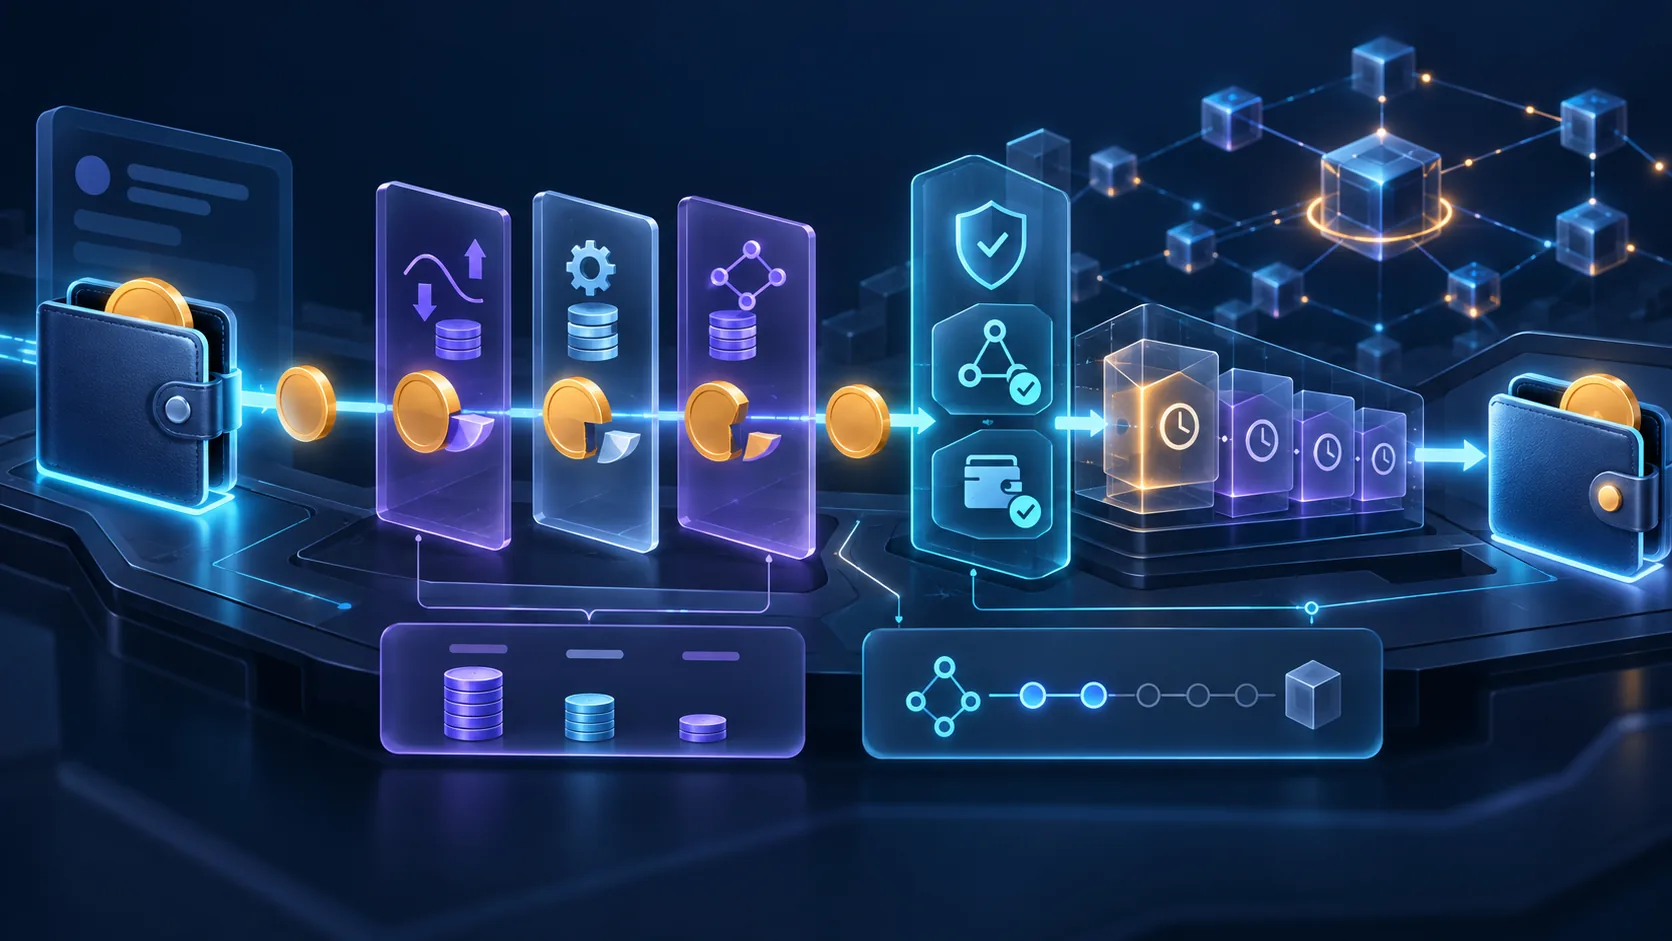
Under ERC-4337 a UserOperation may pass through a bundler and paymaster. Check sponsorship terms and what happens if those services stop.
Upgrades
An upgradeable account can receive fixes but also change its rules. Inspect administrators, delays, audits and the exit path before an upgrade.
Test recovery before an incident
A guardian or delay process may be too slow or unavailable when needed. Run a documented small-scale test and identify relay and upgrade powers.
- Keep an exit route if the relay service stops.
- Check which session keys remain active after recovery.
Practical case: decision and limits
A smart account offers guardian recovery. Check the approval threshold, delay, cancellation route and guardian powers. Test with a low-value account before relying on it. A gas sponsor may refuse an operation without changing asset ownership; service availability, signature validity and account control are separate. Also inspect upgrade rights.
EIP-7702: code delegation retains a master key
EIP-7702 lets an existing Ethereum account delegate execution to code. The original key retains control: a delegated multisig policy does not neutralize that key. Check delegated code, network scope and delegation removal; revoking ERC-20 allowance is a different action.
A concrete verification
Inventory master key, modules, guardians and delegation: visible approvals do not prove two-key control of every spending path.
Hypothetical case: a multisig interface with a critical master key
An Ethereum account delegates execution to EIP-7702 code showing a multisig policy. The EOA key nevertheless remains critical to delegation authorizations. It is misleading to call that key powerless just because the interface requires several confirmations. Compare account authority, delegated code and upgrade procedure; “multisig” alone does not describe the complete control surface.
- Identify the account signing authorization and the actual delegated contract on that network.
- Record who can change delegation and how to check the resulting state.
- Separate delegation removal, policy changes and ERC-20 revocation; one does not establish the others.
Trace a UserOperation through to its outcome
Under ERC-4337, a bundler can group several UserOperations in one transaction calling EntryPoint. Keep the operation identifier shown by the wallet, then record the hash of the transaction that included it. A successful bundle transaction can contain a failed operation. Check your operation’s status in a compatible service’s receipt or in the EntryPoint events, then verify the expected result, such as the amount received.
Checks to make
| Topic | Check |
|---|---|
| Signing rules | Identify signers |
| Recovery | Test the process |
| Fees and relays | Map dependencies |
| Upgrades | Review authority |
Frequently asked questions
Does a recovery phrase always disappear?
No. Recovery design varies and may still rely on secrets.
Are gasless operations free?
No. Fees are sponsored, shifted or charged elsewhere depending on the service.
Verifiable sources
 Ethereum Improvement Proposals: ERC-4337
- Ethereum.org: Accounts
- EIP-7702: Account code delegation
- ERC-7769 draft: UserOperation receipts
Independent educational content reviewed against primary documentation. No personalized recommendation or promise of returns. Updated November 15, 2026
Prepare and continue reading
Useful background
- How to choose a crypto wallet
A crypto wallet manages the keys that authorize operations; it does not physically hold the assets. The right choice depends on use, value at risk and your ability to protect a recovery phrase without sharing it.
- Smart contracts and tokens: read the rules before signing
A smart contract is a program executed by a blockchain. A token is a record managed by a contract under a standard. Before interacting, verify the contract address, network, called functions, approvals, administrator powers and external dependencies.
Continue to the next step
- Message signatures: login, permits and permissions
No immediate paid transaction does not mean no risk. Inspect request type, domain, network, contract, spender, value and expiry. Reject requests whose scope your wallet cannot explain.
- Token approvals: review and revoke spending permissions
On each network, inspect approved spenders, token and limit. Revoke permissions you no longer need with a trusted tool, then verify the confirmed transaction. If a recovery phrase is exposed, revocation alone is insufficient.