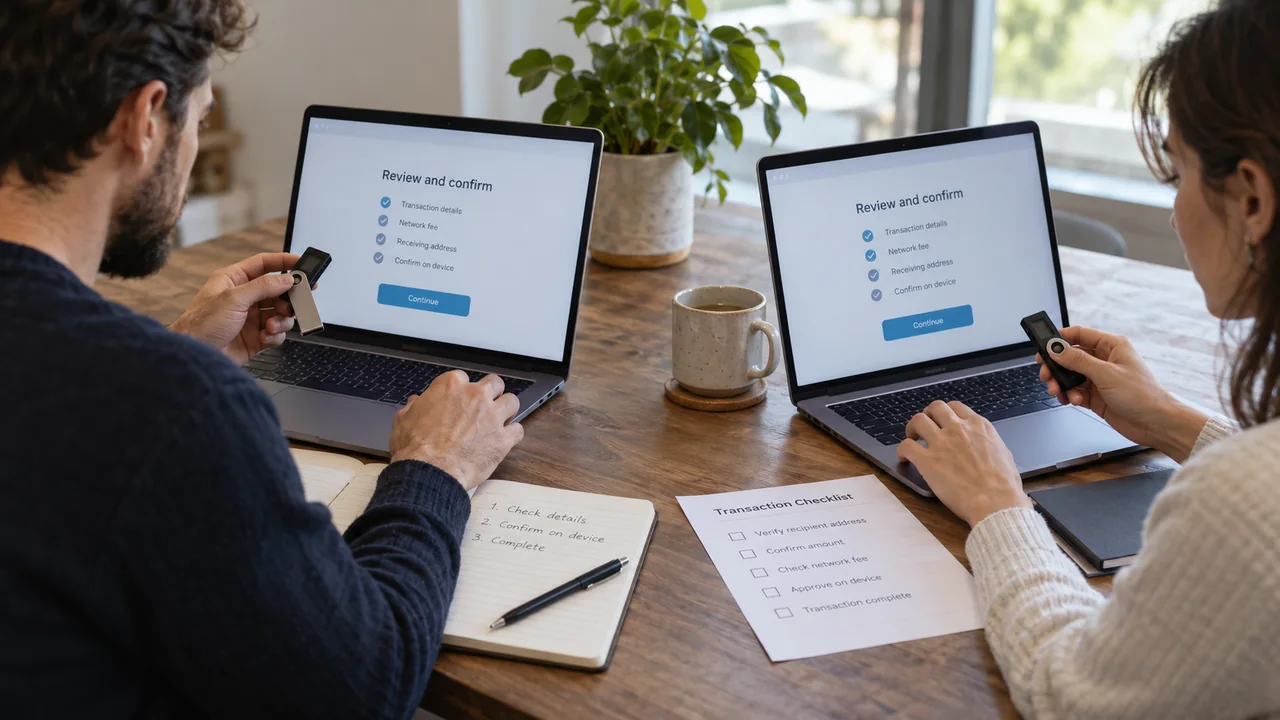
Multisig requires several keys to authorise spending. Security depends on the threshold, independent holders and policy backups as well as the private keys.

Threshold and availability
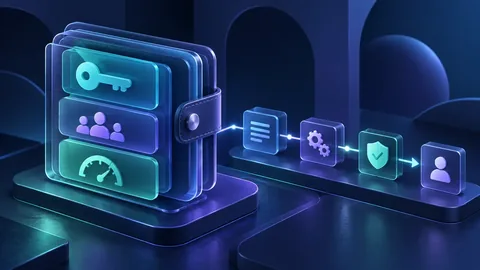
Keys are not the whole wallet
Amount, fee and change
Interpret a 2-of-3 quorum
In a hypothetical 2-of-3 policy, two keys can spend. One unavailable key is tolerable; losing two may lock funds, while compromising two may enable theft. A threshold does not distinguish colocated devices from truly independent holders. Consider fire, theft, human error and simultaneous absence before choosing locations.
Back up the policy
A Bitcoin descriptor can describe public keys, derivation paths, scripts and rules used to recognise wallet outputs. Individual seed backups may not easily reconstruct the collective wallet alone. Keep the exact policy and recovery instructions compatible with your tools. Extended public keys cannot sign, but disclosure can reveal wallet activity.
Verify each proposed spend
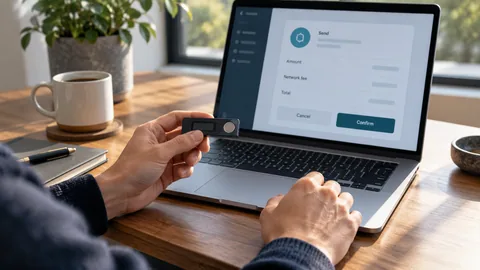
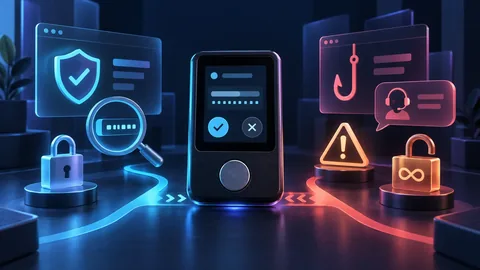
A PSBT carries a partially signed transaction and information needed for signing. Each participant should verify recipient, amount, fee and change on a trusted display. Multiple signatures do not help when everyone blindly approves the same misleading proposal. The coordinator should not be the only place that holds the policy or verifies details.
Practise with an absent signer
Start with a small test wallet. Receive limited funds, make a normal spend and then simulate one signer’s absence using remaining keys and the backed-up policy. Verify software compatibility and participants’ understanding. Untested backups may be incomplete; keep exercises separate from primary funds.
Distinguish scripts from contracts
Bitcoin script policies and smart-contract collective accounts do not share every property. For contract accounts, inspect modules, owners, thresholds, upgrade mechanisms and network. Message signatures may have application-specific consequences. Read the chosen system’s documentation: the word multisig guarantees neither harmless modules nor automatic recovery.
Prepare policy changes
Changing a Bitcoin policy generally means moving outputs to a new policy. Contract accounts may update owners or thresholds through different procedures. Document proposal, independent review, refusal handling and unavailable signers. During incidents, verify the replacement address and retain needed backups before rotating.
A concrete verification
Test a small spend with an absent signer: three devices do not prove independent 2-of-3 control.
A transaction proposal is not an approval
A PSBT carries information needed to construct and sign a Bitcoin transaction. Each signer must still verify recipients, amounts, fees and change. A coordinator’s name for an output does not prove ownership.
- Recognise change using the expected policy and keys.
- Check the content on a trusted display before signing.
Worked example: two signatures, one shared mistake
In a 2-of-3 setup, two people relying on the same compromised screen can approve the same mistake. A signature threshold does not replace independent verification.
- Plan checks on signing devices and back up the wallet policy.
- Rehearse the process with one signer absent, without sharing secrets between participants.
Verify the change output in a PSBT
For a Bitcoin multisignature wallet, a PSBT includes the proposed outputs and can carry derivation information. Before signing, verify change against the wallet policy registered on the signing device or with a separate trusted tool. Match every external output to an intended recipient and check the total fee. A change label shown by the software that prepared the PSBT calls for independent verification.
Scenarios and model limits
| Situation | Interpretation |
|---|---|
| 2-of-3: one unavailable key | Remaining keys and policy can enable spending. |
| 2-of-3: two lost keys | Threshold not met; funds may be locked. |
| 2-of-3: two compromised keys | An attacker may meet the spending threshold. |
Frequently asked questions
Are two devices automatically safe?
No. Shared location, seed or operator can create a common failure point.
Is a PSBT itself an authorisation?
No. It transports transaction data; required signatures and transaction validity still matter.
Should public keys be protected?
They cannot sign, but may reveal wallet activity. Limit disclosure and retain policy backups.
Verifiable sources
 Bitcoin Developer Guide: Wallets
- BIP-174: Partially Signed Bitcoin Transaction
- Bitcoin Core: Output descriptors
- Safe: Smart account architecture
Independent educational content reviewed against primary documentation. No personalized recommendation or promise of returns. Updated November 15, 2026
Prepare and continue reading
Useful background
- How to choose a crypto wallet
A crypto wallet manages the keys that authorize operations; it does not physically hold the assets. The right choice depends on use, value at risk and your ability to protect a recovery phrase without sharing it.
- Hardware wallet: setup, backup and first transfer
Buy through a verifiable channel, initialize the device yourself, keep the recovery phrase offline and make a small test transfer. Confirm address and details on the device screen.
Continue to the next step
- Crypto backup and inheritance: preserve access without exposing keys
A sound plan separates inventory, secrets and instructions. It uses protected redundant copies, distinct people or roles, a tested recovery procedure and regular reviews. Never keep the recovery phrase, access code and complete instructions together.
- DAO governance: from visible votes to power actually exercised
A DAO usually combines discussion, voting, delegation, contracts and signers. A governance token does not prove that every vote automatically executes a decision. Check who proposes, votes, can veto, holds keys and controls treasury execution.